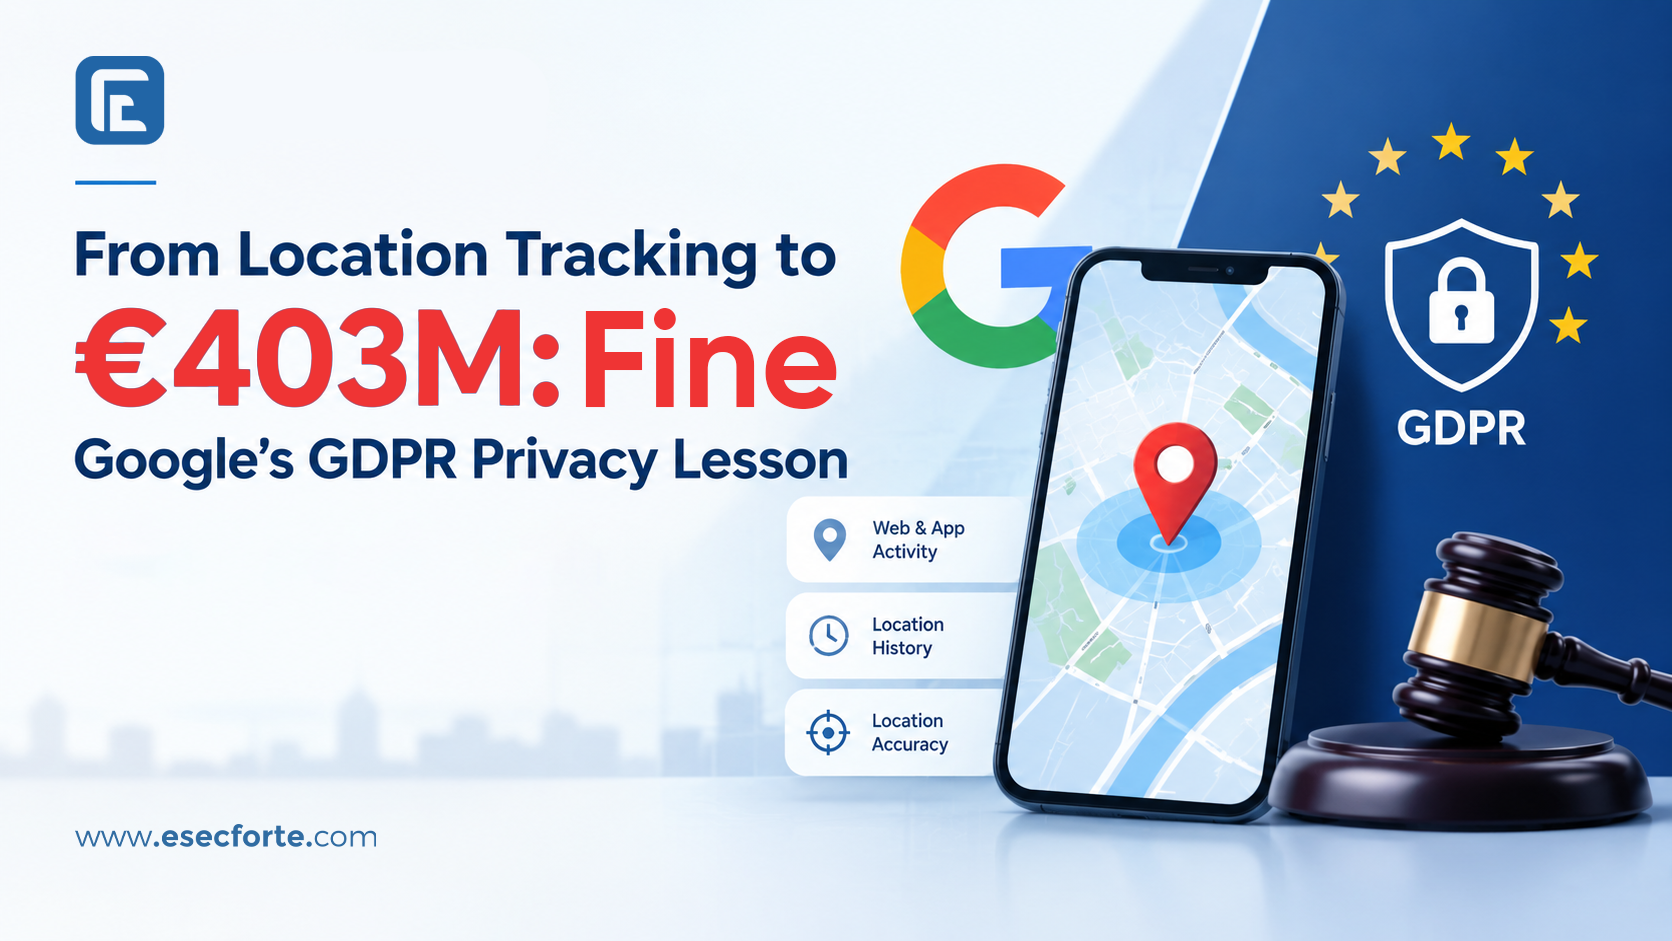
From Location Tracking to €403M: Google’s GDPR Privacy Lesson
Google has been fined €403 million (44 Billion INR) by Ireland’s Data Protection Commission (DPC) after an investigation found that the company breached EU’s GDPR requirements in its handling of users’ location data.
The ruling highlights a growing concern in the digital economy: how much do users really know about the personal data being collected about them; and how long that data is kept?
The DPC’s investigation, which began in February 2020, examined Google’s processing of location information through three key features: Web & App Activity, Location History, and Location Accuracy.
The inquiry covered the period from May 25, 2018, when the GDPR came into force, to February 4, 2020.
What Did the DPC Find?
According to the Irish regulator, Google’s practices did not provide users with sufficient clarity or control over how their location information was processed.
The DPC concluded that Google violated the GDPR in four key areas:
- Lawfulness and fairness: The processing of location data through Web & App Activity and Location History did not meet GDPR requirements for lawful and fair processing.
- Accountability: Google was unable to demonstrate compliance with the lawfulness, fairness and transparency requirements concerning Location Accuracy.
- Transparency: The company did not provide sufficient transparency around the processing of location data across the three features.
- Data retention: Location information collected through Web & App Activity and Location History was retained for longer than necessary.
The regulator was particularly concerned that users could have been unaware that their location information might be used to help influence advertising or infer information about their interests.
That lack of awareness, the DPC said, could ultimately reduce an individual’s ability to control their own personal data.
Why Location Data Is So Sensitive
Location information can reveal far more than simply where someone happens to be.
Repeated location data can potentially provide insight into a person’s routines, places they visit, workplaces, interests and other aspects of their private life.
Graham Doyle, Deputy Commissioner of the Irish DPC, emphasized this point while commenting on the decision.
“Location data can bring both benefits and harms to individuals.”
According to Doyle, location information can make online services more useful, but it can also reveal significant and sometimes inherently private information about an individual.
That tension sits at the heart of the broader debate surrounding digital privacy: the same data that makes technology more personalized can also make users more exposed.
Google Says Its Practices Have Changed
Google pushed back on the implications of the ruling by emphasizing that the case concerns historical practices.
A company spokesperson said:
“This case centers around historical policies that have since been updated.”
Google added that, beginning in 2019, it significantly changed its approach and introduced tools designed to make managing location data easier for users.
The distinction is important. The DPC investigation focused specifically on Google’s practices between 2018 and early 2020, rather than necessarily describing the company’s current location-data practices.
Google Given Six Months to Comply
Alongside the €403 million (44 Billion INR) penalty, the DPC ordered Google to bring its processing practices into compliance within six months.
The decision therefore goes beyond a financial penalty. It also requires changes to how the company handles the relevant personal data.
For users, the case underscores an increasingly important question: when a service asks for access to location information, is consent genuinely informed if the consequences of sharing that data aren’t clear?
The Bigger Privacy Question
The Google case isn’t simply about one feature, one setting or one fine.
It reflects a broader challenge created by modern digital services: personalization depends heavily on data, but meaningful personalization requires users to understand what they’re giving up in return.
GDPR places significant emphasis on transparency, accountability and users’ control over their personal information. The DPC’s decision shows that regulators are prepared to scrutinize not only whether companies collect personal data, but also how clearly they explain that collection, how long they retain the information, and whether users can meaningfully understand and control the process.
For consumers, that makes location settings more than a technical preference buried inside a smartphone menu. They are part of a much larger conversation about who controls personal data in an increasingly data-driven world.